Solved the issue where frp cannot transparently transmit IP
During the process of improving the demo, I encountered some issues. The biggest and most serious one is that frp's default settings cannot pass through IP addresses, which caused the attack defense based on IP address duplicate registration and access to fail (the backend could only see 127.0.0.1).
After exploring, it turns out that sakura-frp's documentation does support IP address passthrough. The documentation actually has fairly clear instructions: 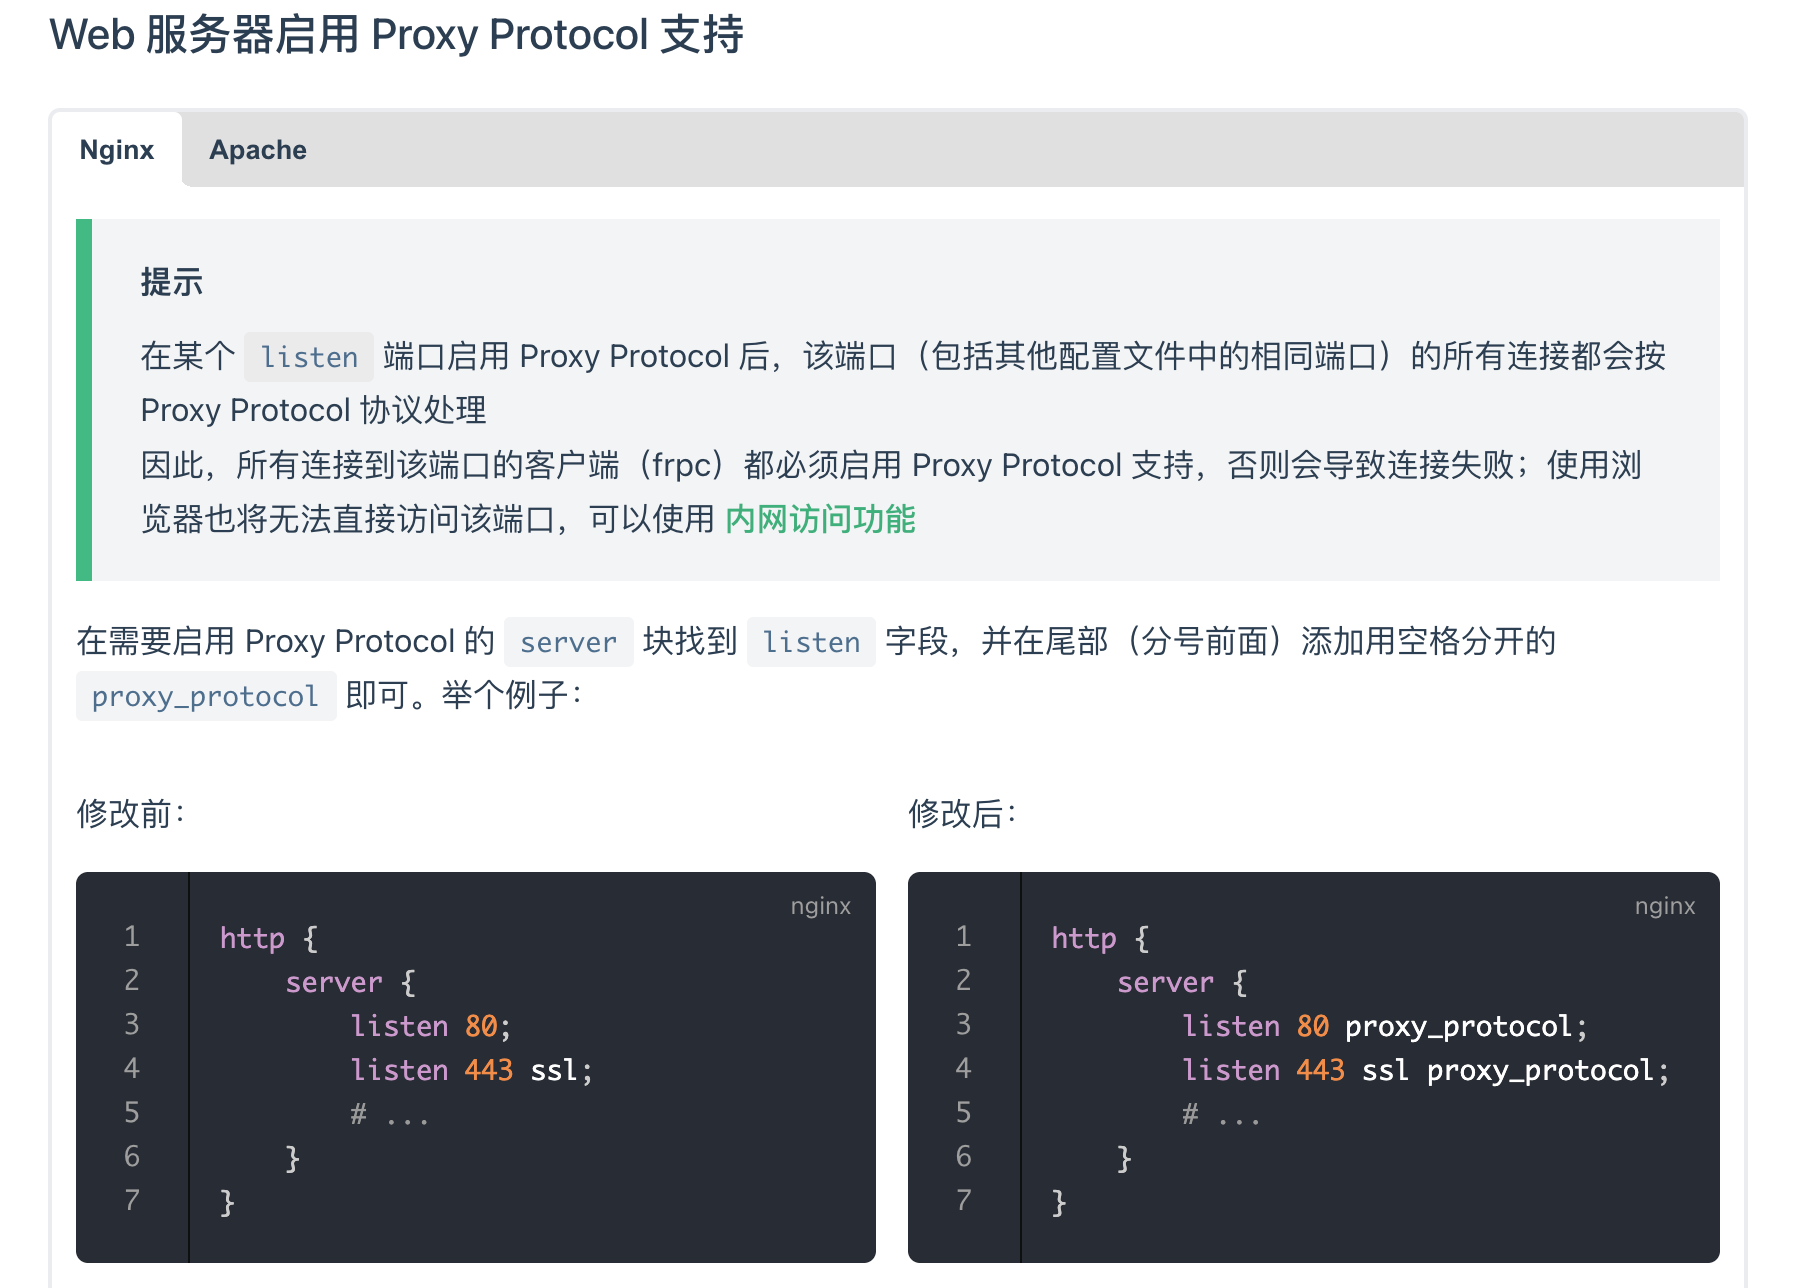
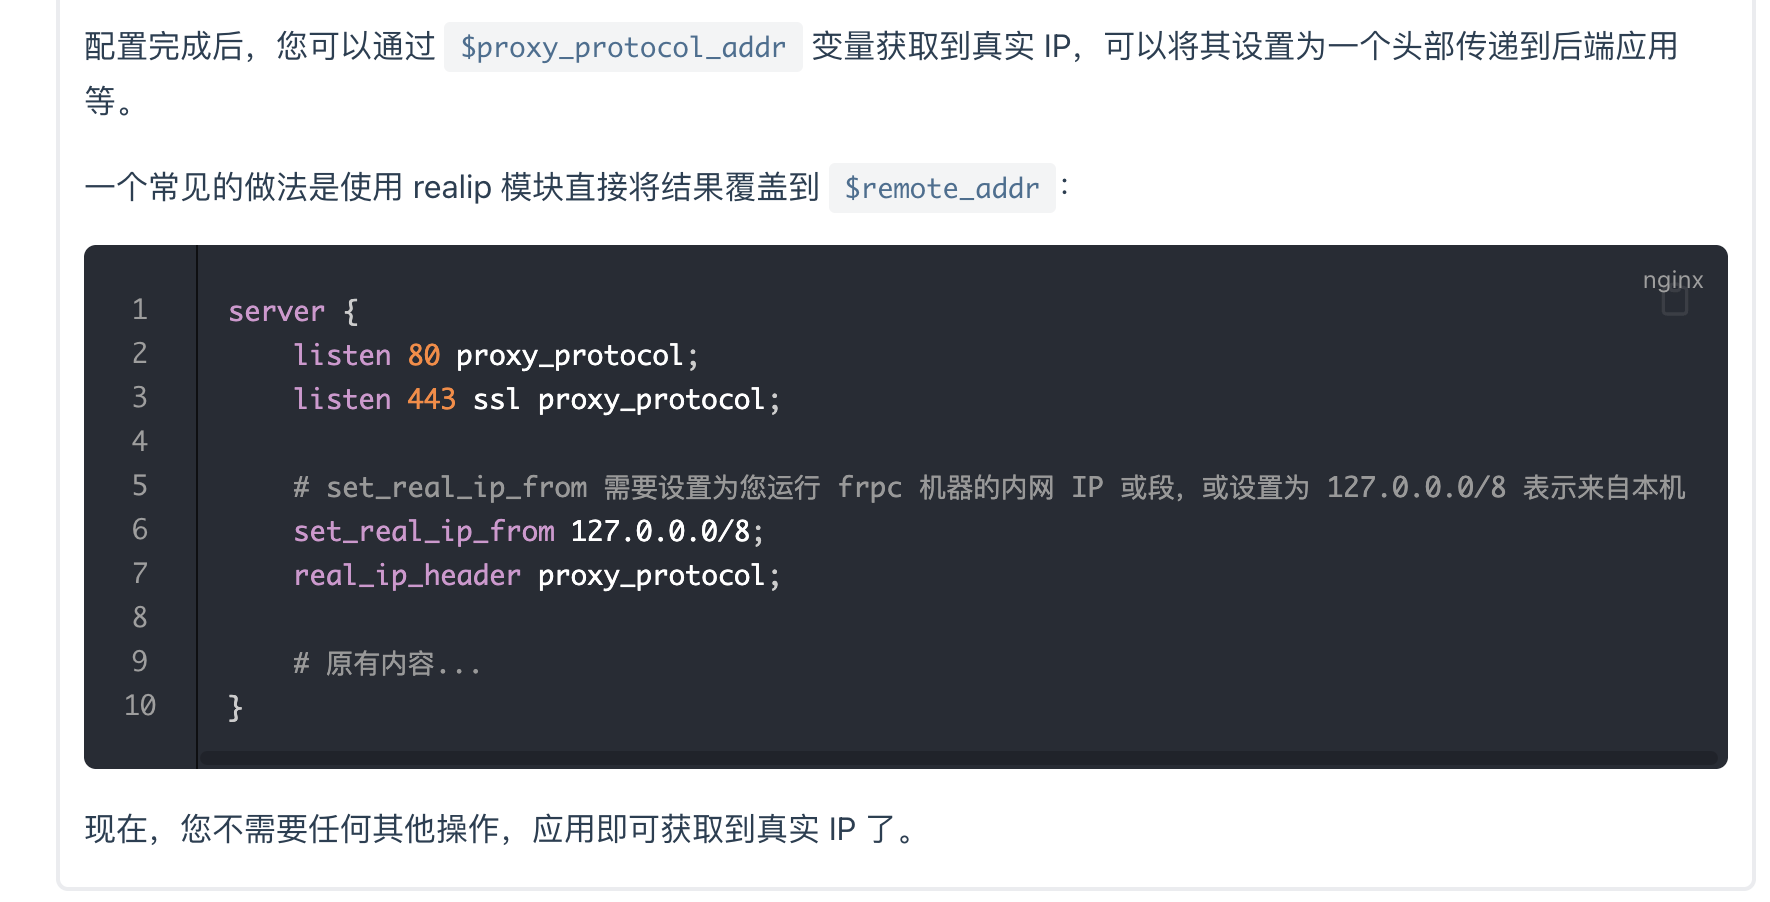 After enabling PP on the server side, add the settings on the sakura-frp panel:
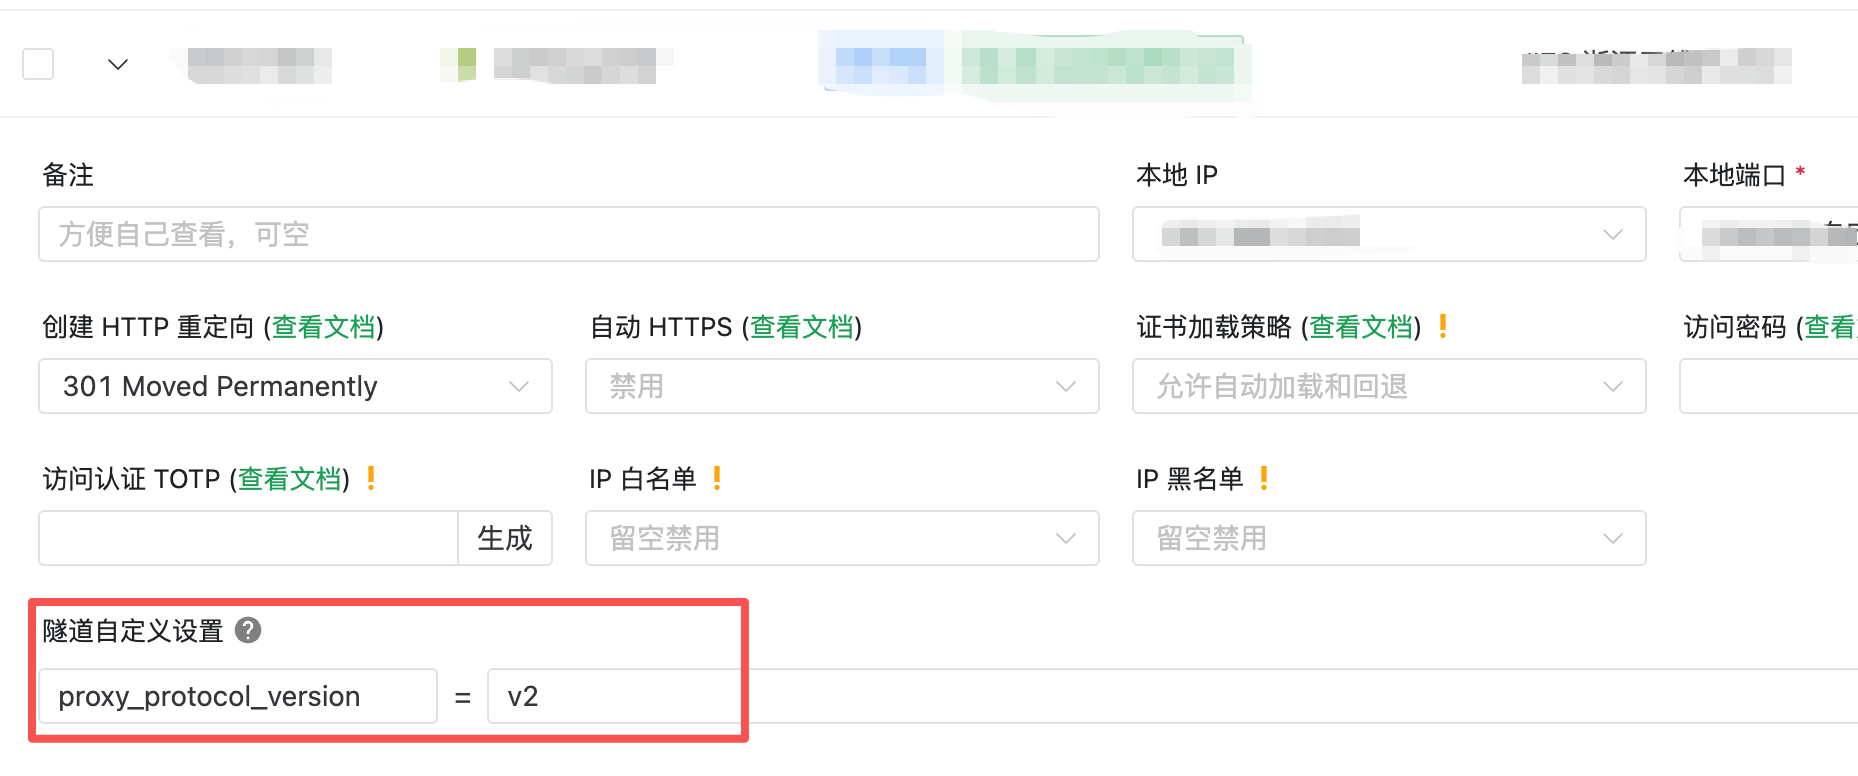 Because modifying the PP proxy, if the agent operates it themselves, they might add SSL configuration or forwarding, which would change the port. Just let them change it themselves.
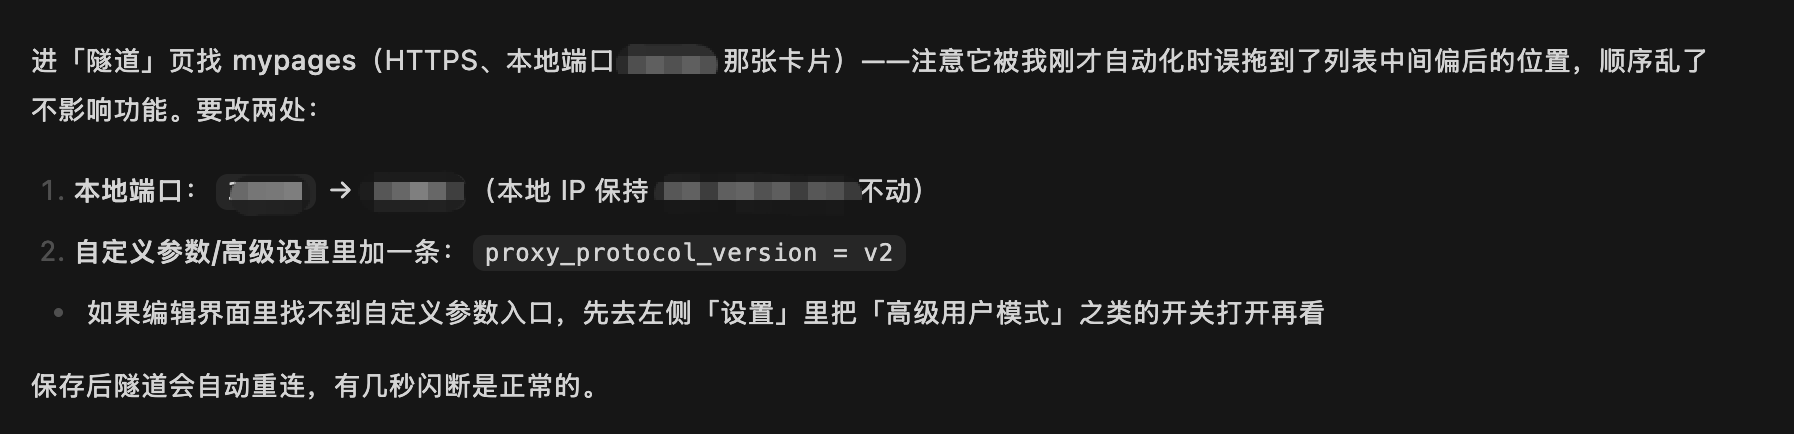 Actually, GLM helped with the settings. It's just that sakura-frp itself doesn't support CLI to directly modify configuration files, otherwise it would have been fully automated. After completion, you can get the access IP normally:
 I tested with recknerd and JD Cloud servers, and all source IPs can truly reach the backend.
Comments
Leave a comment (email only, never shown)
No comments yet.